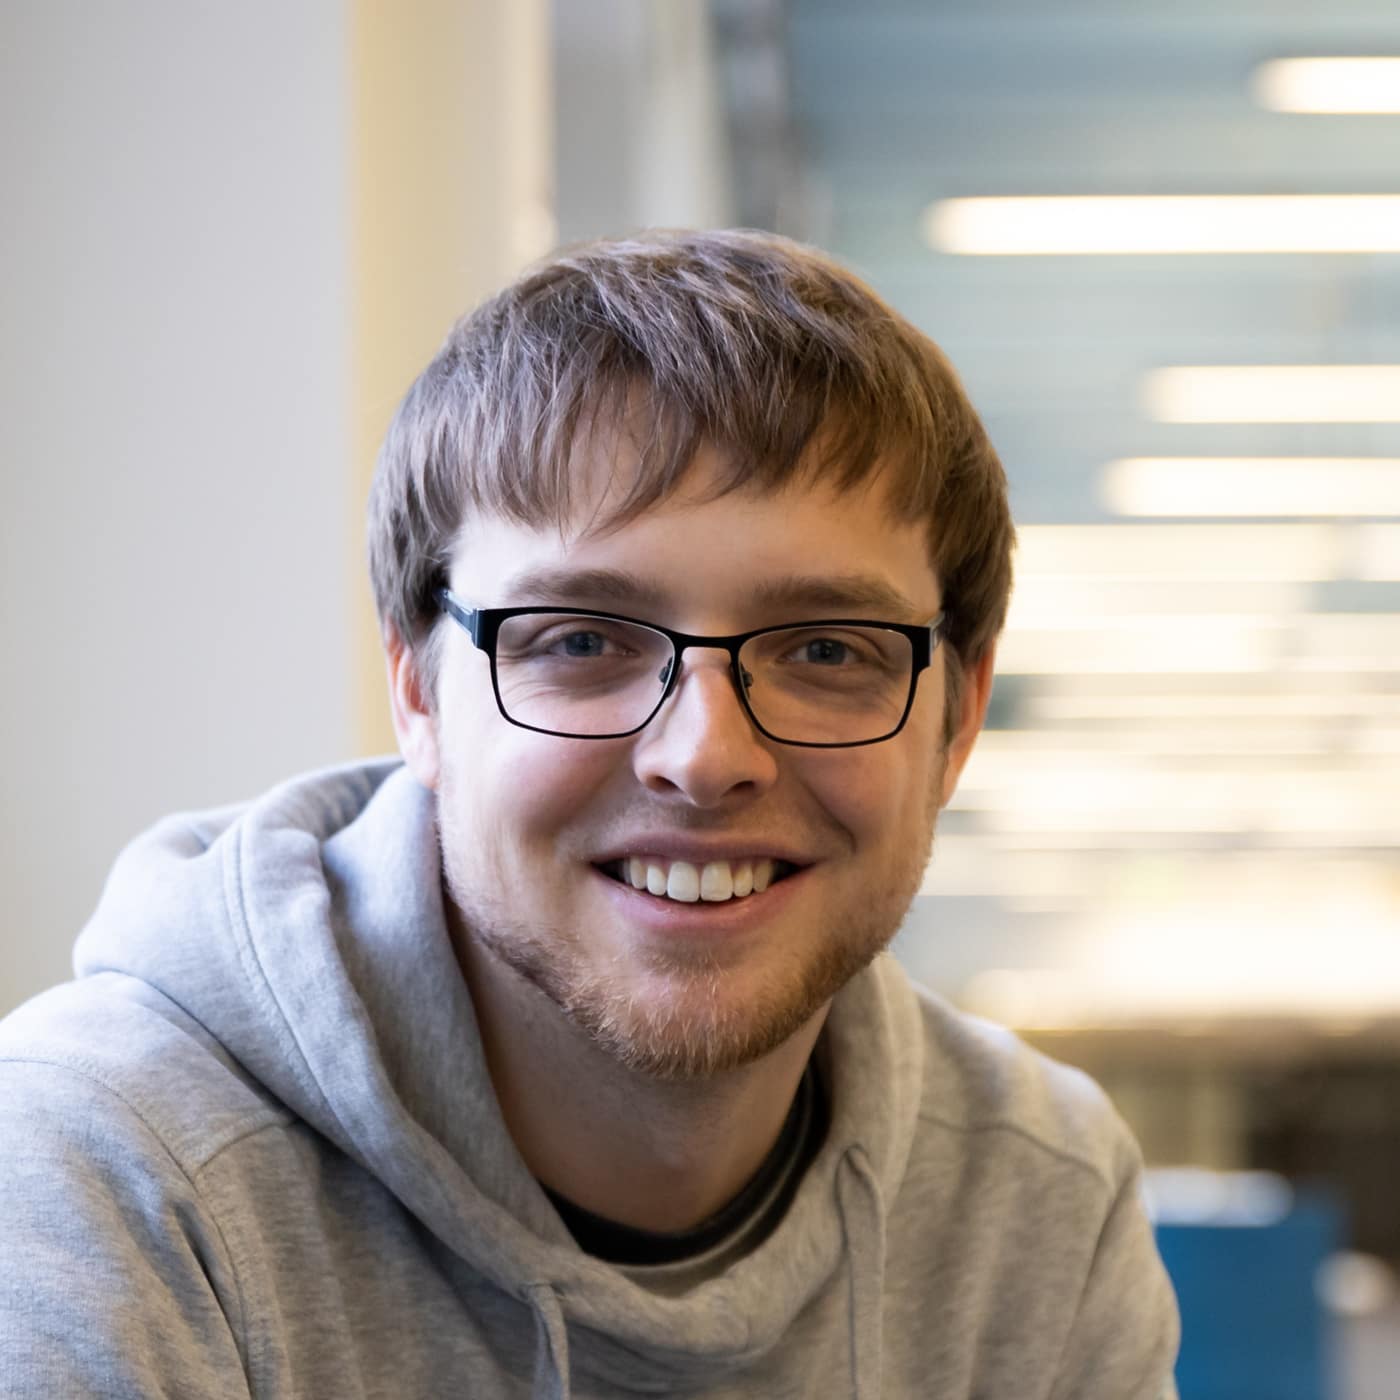
Dr. Tobias Scharnowski has built his career around a simple but important question: what happens when software behaves differently from how it was expected to behave? As co-founder and CEO of Fuzzware, he works at the intersection of academic research, vulnerability research, and practical cybersecurity. His focus is embedded software, the code that controls products such as vehicles, medical devices, and industrial systems.
Dr. Tobias Scharnowski | Co-founder and CEO | Fuzzware
EliteX proudly features Dr. Tobias Scharnowski in this edition, recognizing a distinguished journey of leadership, innovation, and meaningful impact.
His journey began in academic research at CISPA, where he worked on automated analysis of embedded software. His research focused on making firmware easier to test for security vulnerabilities. Along with Simon Wörner, he later founded Fuzzware based in Bochum, Germany, to bring that research into industry. Today, the company helps manufacturers identify weaknesses in the software controlling their products before those weaknesses can create risks for customers.
Firmware security starts with understanding how software behaves in the real world.
For Scharnowski, cybersecurity is driven by technical curiosity as well as responsibility. He is particularly interested in the gap between how a system is designed to work and what it actually allows. Investigating that gap can reveal unexpected behavior and security weaknesses. Embedded security makes this challenge especially meaningful because software is connected to physical products and processes. A weakness in firmware can have consequences beyond a computer screen.
One of the biggest challenges in his journey was turning research into technology that engineering teams could use in their everyday work. A research prototype can prove that an idea works, but a commercial product needs to be reliable, practical, and understandable. Engineers need results that fit into their existing processes and help them solve real problems. Moving from research to entrepreneurship also meant taking responsibility for customer relationships, hiring, and financial planning.
This practical approach is central to Fuzzware. Firmware is difficult to test because it is closely connected to the hardware for which it was designed. It may expect specific peripherals, interrupts, and other hardware interactions. Running the same software on a standard computer is therefore not straightforward. Testing directly on physical devices can also make large-scale automated testing difficult.
Fuzzware addresses this challenge through rehosting, allowing supported firmware to run in a virtual environment. Its approach automatically models hardware interactions based on how the firmware uses them. This creates an environment where researchers and engineering teams can conduct extensive automated testing without needing a separate physical device for every test.
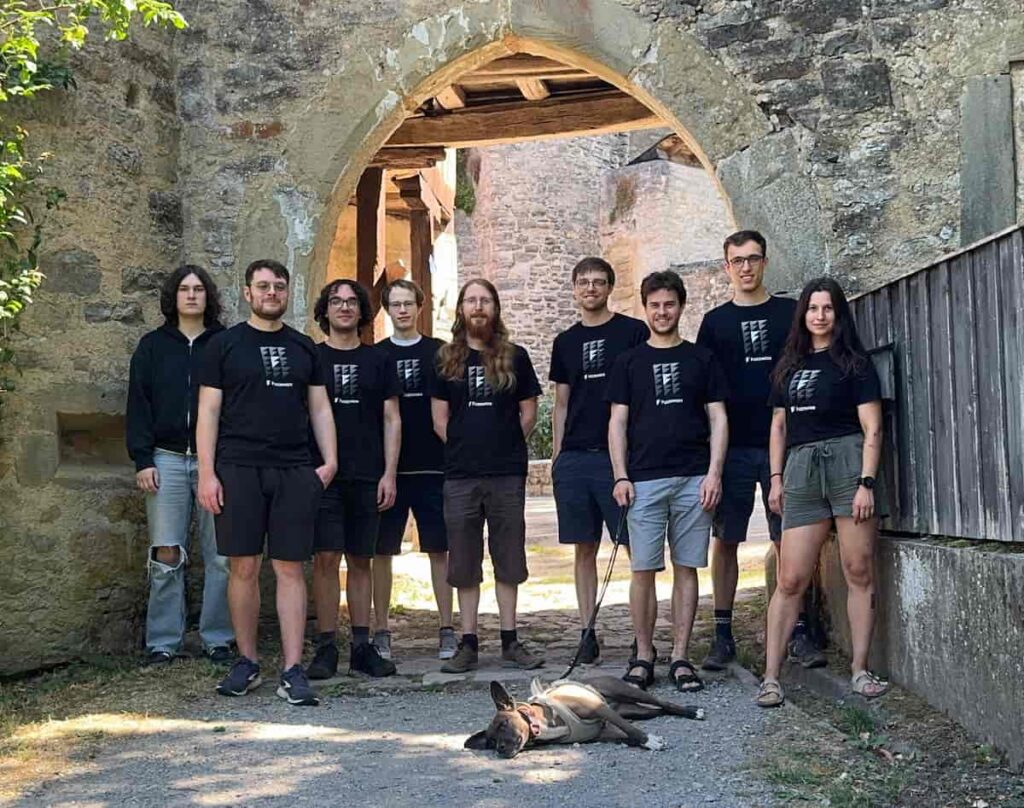
Fuzzing is an important part of this process. Instead of relying only on expected inputs, fuzzing provides software with large numbers of unexpected inputs and observes how it responds. This can expose failures that traditional functional testing may never reach. When a potential vulnerability is discovered, the process can continue through investigation, reproducible findings, remediation, and retesting after a fix.
Scharnowski also sees value in combining different forms of testing rather than treating them as alternatives. Physical-device testing remains important. Fuzzware adds hardware-free testing of binary firmware on standard computing infrastructure. This full-system testing explores interactions between application code, libraries, and interrupt handlers that may be missed by isolated component testing. At the same time, physical testing remains valuable for hardware behavior that emulation cannot completely reproduce.
The goal is not only to find vulnerabilities, but to help engineers fix them.
For products that combine software from several suppliers, Scharnowski emphasizes traceability and clear responsibility. Manufacturers need to know exactly which software versions are integrated, what was tested, under which conditions, and what remained outside the testing scope. Integrated firmware testing is particularly important because individual components can behave differently when combined. Binary analysis can also provide useful insight when source code is unavailable.
His work has already produced significant research results. The original Fuzzware research, presented at USENIX Security in 2022, demonstrated how automated hardware modeling could improve firmware fuzzing. In that evaluation, Fuzzware discovered 15 previously unknown bugs, with 12 CVE identifiers assigned. The project also received a Distinguished Artifact Award. For Scharnowski, however, the achievement is not limited to the research itself. Building a company around that work has created a way for engineering teams to apply the technology to real products.
Looking ahead, he sees opportunities for AI to support firmware security research by helping researchers navigate unfamiliar code, suggest test cases, and organize findings. Yet he believes useful results still need to be reproducible and properly validated. A suspected vulnerability should have a reproducible test and a clear explanation of the conditions required to trigger it. Proposed fixes should also be tested against the original failure and checked for regressions.
His broader goal is to make continuous firmware security testing a normal part of product development. Testing should be repeatable across builds, results should reach the engineers responsible for fixing problems, and teams should understand both what has been tested and where gaps remain.
Scharnowski also wants Europe to become stronger at turning cybersecurity research into successful products. He sees collaboration between researchers, manufacturers, young companies, and public institutions as an important part of that process. His vision is a European technology ecosystem where companies of different sizes can access advanced security testing and build products with security considered throughout their development and maintenance.
Security research creates real value when it reaches the engineers building products.
More information on Fuzzware can be found at https://fuzzware.io or via LinkedIn.